The Full Compliance Stack an Independent Mortgage Banker Must Maintain to Protect GSE Seller-Servicer Standing
Independent mortgage bankers must layer financial audits, outsourced controls.
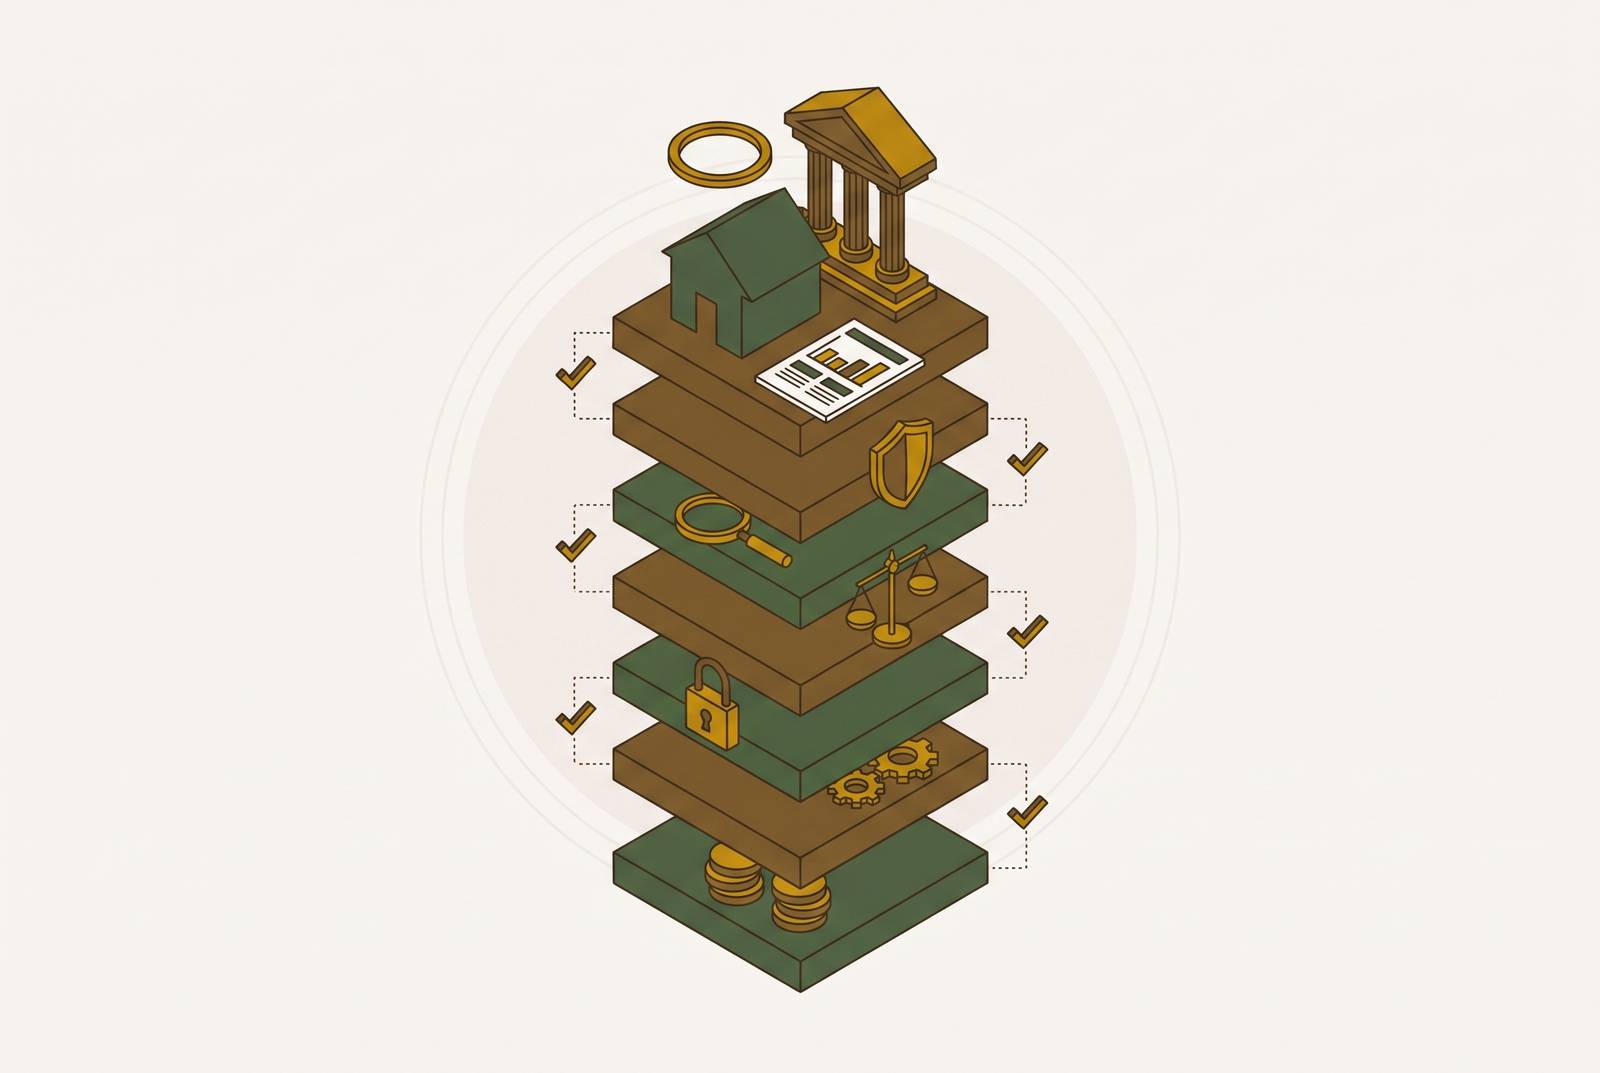
Mortgage banking audit and compliance services for independent mortgage bankers must connect financial assurance, outsourced controls, servicing data, and AI governance, with a separate HUD reporting regime where applicable. GSE seller-servicer standing depends on maintaining those layers together. A gap in any contractual condition can threaten the secondary-market access on which an IMB’s business depends.
Why GSE seller-servicer standing is a contractual relationship, not a regulatory one
An independent mortgage banker has substantive obligations resembling those of a regulated institution, but no bank charter and no prudential supervisor. For GSE eligibility, the governing instruments are the Fannie Mae Selling Guide and Freddie Mac Single-Family Seller/Servicer Guide. The distinction changes how compliance failure becomes a business threat. The enforcement mechanism here is contractual.
The Fannie Mae Selling Guide treats failure to maintain an eligibility requirement or comply with the Lender Contract as a breach of that contract. Freddie Mac’s Guide provides for remediation requirements, suspension, or revocation of approved status. What does revocation mean for a lender dependent on secondary-market access? It can effectively shut down operations. These GSE conditions are therefore not optional guidance, although federally governed obligations, including HUD requirements, form a separate part of the broader compliance stack.
The financial floor — minimum net worth, liquidity, and capital requirements that must hold continuously
Non-depository seller/servicers must maintain Adjusted Net Worth of at least $2.5 million, plus additional percentages of residential first-lien mortgage servicing unpaid principal balance, or UPB, serviced for Fannie Mae and Freddie Mac. A higher percentage applies to UPB serviced for Ginnie Mae. They must also maintain a minimum Adjusted Net Worth-to-total-assets ratio. These are continuous requirements. A breach can occur anywhere in the calendar year.
Liquidity has its own requirements that net worth alone does not meet. Allowable Liquidity requirements apply specified percentages to UPB, with distinct rates for scheduled/scheduled remittances and Ginnie Mae UPB. Large non-depository seller/servicers also face supplemental Allowable Liquidity requirements calculated against Fannie Mae/Freddie Mac residential first-lien servicing UPB.
Large non-depository seller/servicers must also submit a capital and liquidity plan to Fannie Mae within the required period after each calendar year-end. That plan covers governance, risk management, liquidity risk monitoring, contingency funding, and an annual liquidity stress test that includes mortgage servicing rights value under an adverse scenario. Because the thresholds are calculated under GAAP, independent CPA assurance is needed to verify the reported amounts, and lenders must keep checking between reporting dates to stay in compliance.
How do you find a CPA firm that understands GSE audit requirements and internal audit independence?
GAAP-based audited financial statements provide the evidence through which an IMB demonstrates its financial position to GSEs, warehouse lenders, and investors. The external examiner must understand mortgage servicing rights valuation, gain-on-sale treatment, and warehouse line accounting. Knowledge of these mortgage-specific accounting areas provides concrete criteria for assessing a CPA firm’s fit.
The GSE Guides require internal audit and management control procedures that check the overall quality of loan production and servicing. The audit function cannot share reporting lines with the areas it reviews and must report directly to senior management and/or the board. Independence is part of the contractual requirement. An audit function can breach Guide requirements if it reports through the business-line head whose work it reviews, even when the financial statements are accurate.
The SOC 1 and SOC 2 layer — outsourced processing creates financial-reporting dependency that makes these examinations mandatory
Outsourcing changes where processing occurs while leaving accountability with the lender. Most IMBs rely on outside providers for critical work, including subservicing, loan-origination platforms, pricing, hedging, and valuation. Those dependencies make service-organization controls examinations a practical necessity. SOC 1 addresses services that could affect the client’s financial reporting, including transaction processing and the systems supporting it. SOC 2 Type II addresses security, availability, processing integrity, confidentiality, and privacy across the same infrastructure.
A SOC 1 Type II report examines whether controls operated effectively over an extended period, which is the standard GSEs and institutional investors require and expect. A Type I report addresses a point in time and does not provide equivalent evidence. For mortgage servicing, substantive control objectives include accurate loan boarding, payment application, escrow administration, and investor reporting and remittance. They also encompass default and loss-mitigation accounting, including delinquency coding and modification effective dates.
Dovenmuehle Mortgage, Inc. completed its 2025 SOC 1 Type 2 and SOC 2 Type 2 audits. For an IMB using Dovenmuehle or another subservicer, the practical obligation is to obtain and review those reports annually as part of vendor oversight. Access management, change management, and incident response are relevant to both reports, so a coordinated dual-report engagement can test overlapping controls once.
The real-time data reporting layer — GSE transitions to event-driven submission that existing batch systems cannot handle
Fannie Mae and Freddie Mac are moving from legacy batch reporting toward submissions that are event-driven and near-real-time. That transition reaches across servicing systems and imposes contractual deadlines. It is not simply a discretionary technology upgrade. Servicers that handle both portfolios must meet overlapping requirements on different timelines, and development and testing take up some of the time they have to put the changes in place. As amnesty windows expire, servicers have even less time to delay.
Existing processes must meet the new timing and precision requirements. Batch-era reporting controls cannot be assumed to work under an event-driven model merely because their prior outputs were acceptable. Timing becomes part of the compliance test. SOC 1 examinations already cover investor reporting and remittance, so the new reporting flows change what those controls must do. A technology transition can therefore expose an audit weakness as well as a submission failure.
The HUD Section 232 parallel stack — FHA-approved IMBs face a separate federal audit and reporting regime
For federally approved IMBs originating and servicing HUD Section 232-insured loans, the stack extends beyond GSE contracts. Section 232 covers facilities that provide skilled nursing, assisted living, intermediate care, and board-and-care. Its federal reporting obligations run in parallel with GSE requirements. They are not satisfied by GSE compliance.
24 CFR 5.801 requires borrowers to provide HUD and the lender with an audited annual financial report based on examination of their books and records. HUD’s Uniform Financial Reporting Standards require annual financial statements within 90 calendar days of the fiscal-year-end quarter, prepared under GAAP as further defined by HUD’s supplementary guidance. Operators must send quarterly statements within 60 calendar days of each fiscal quarter-end, but they have 90 calendar days for the final quarter. HUD can require more frequent or audited statements case by case. A covenant breach, occupancy decline, or unreliable submission can trigger that additional scrutiny.
HUD OIG completed Report No. 2026-BO-0001 in 2026 to assess whether ORCF adequately identifies and mitigates Section 232 portfolio-level risks. That oversight makes underwriting files and post-closing monitoring relevant beyond annual deadlines. The practical response is a reporting calendar covering annual filings, operator quarterly statements, and ad hoc HUD requests, supported by auditors who understand GAAP, ORCF requirements, and HUD’s supplementary reporting standards.
The AI governance layer — what Freddie Mac Bulletin 2025-16 and Fannie Mae LL-2026-04 require as contractual conditions
Freddie Mac Bulletin 2025-16, issued December 3, 2025, amended Guide Sections 1302.2 and 1302.8 and took effect March 3, 2026. Fannie Mae Lender Letter LL-2026-04, issued April 8, 2026, took effect August 6, 2026, 120 days after publication. Both make AI governance a contractual condition. Their scope includes AI and machine learning used in originating loans sold to, or servicing loans for, either GSE, including AI embedded in vendor platforms.
Both frameworks require policy governance and ongoing risk management, but they differ in prescription. Freddie Mac requires senior-management approval, at minimum from the CIO, CTO, CISO, or CRO, communication to responsible personnel, and a named policy owner conducting at least annual reviews. Fannie Mae requires transparent policies covering development, implementation, use, and maintenance, incorporating trustworthy and ethical AI characteristics. The distinction affects how a lender demonstrates compliance. Freddie Mac specifies segregation of duties and documented accountability, while Fannie Mae’s principles-based approach leaves more of the governance design to the lender.
Freddie Mac also specifies assessment of threats such as data poisoning and adversarial inputs, regular monitoring for performance, security breaches, and bias, and internal and external audits against standards such as NIST 800-53 and ISO 27001. Fannie Mae requires subcontractor and vendor AI governance that is “no less protective” of its requirements. Freddie Mac’s Guide also covers vendor-embedded AI and requires indemnification for liabilities from AI/ML use, whether or not they could have been foreseen.
Under both frameworks, lenders must promptly disclose on request which types of AI/ML they use, why and how they use them, and what safeguards they have. Fannie Mae additionally requires “such other information as Fannie Mae may require.” This is where policy becomes an evidentiary obligation. Can the lender explain the deployed system, rather than merely produce a policy approving AI use? Building to Freddie Mac’s more prescriptive standard will likely support compliance with Fannie Mae’s framework, but disclosure still depends on access to the underlying information.
Why a vendor’s SOC 2 report no longer satisfies AI governance, and what an AI-specific vendor audit must cover
Lenders still need a vendor’s SOC 2 Type II report, but the AI frameworks raise questions that it does not answer. Its Trust Services Criteria address security, availability, processing integrity, confidentiality, and privacy. They do not substitute for AI-specific vendor diligence. A system can require evidence about model governance, fair-lending testing, or adverse-action explanations that a SOC 2 examination was not designed to provide.
An AI-specific vendor audit must document the production model inventory, including vendor-embedded models, deployed versions, deployment dates, and upstream and downstream dependencies. It must examine development, validation, retraining, and retirement, together with notification before material changes reach deployment. Change control is central to that inquiry. The audit must also establish whether vendors test disparate impact by protected class and make results available to the lender, because ECOA and HMDA exposure remains with the lender. Explainability must extend to whether the system supports an ECOA-compliant adverse action notice.
The U.S. Department of the Treasury released the Financial Services AI Risk Management Framework on February 19, 2026. Developed by the Cyber Risk Institute in coordination with the FSSCC, with input from more than 100 financial institutions, it provides 230 control objectives across Govern, Map, Measure, and Manage. It is voluntary. Lenders can also refer to ISO/IEC 42001 and the emerging AIUC-1 assurance structure, while guidance on how to apply them to mortgages is still being developed.
None of those frameworks substitutes for contractual access. An AI-specific audit must establish whether the vendor agreement lets the lender examine AI governance documentation on demand. The GSE’s disclosure right reaches into the vendor relationship. Most current vendor contracts do not grant the access rights that obligation requires, leaving a gap between what the lender must disclose and what it can obtain.
How the layers interlock, and what a gap in any one of them costs
Audited financial statements depend on reliable servicing data, while SOC 1 examinations address controls over outsourced processing of that data. SOC 1 and SOC 2 controls increasingly operate through AI-assisted systems, which require their own governance. A failure can cross those boundaries. When batch-era investor reporting controls fail to meet event-driven requirements, they create a risk of misstatements in financial statements and the Adjusted Net Worth calculation.
An undisclosed vendor model retrained without the lender’s knowledge creates a different route to breach. The lender may be unable to satisfy an on-demand disclosure request even if no adverse model outcome has occurred. Harm is not the only compliance test. Remediation requirements, suspension, or revocation can follow contractual failures, with consequences shaped by the lender’s dependence on secondary-market access.
The practical response is a shared compliance calendar and professional relationships spanning specialized audit, legal counsel, and compliance advice. Those professionals need skills in mortgage banking accounting, SOC examinations, HUD Section 232 and skilled nursing facility accounting, and emerging AI assurance standards. The decisive question for an IMB selecting advisors is whether they can identify how a weakness in one layer becomes exposure in another before it threatens seller-servicer standing.